Two CVEs. Chained. CVSS 9.8 combined. Ivanti EPMM — the tool that manages your mobile fleet — became the entry point.
CVE-2026-1281 and CVE-2026-1340 are unauthenticated remote code execution vulnerabilities in Ivanti Endpoint Manager Mobile under mass exploitation. GreyNoise telemetry recorded 83% of exploitation sessions originating from a single bulletproof hosting IP on PROSPERO OOO (AS200593), while Shadowserver observed 28,300+ unique source IPs attempting exploitation by February 9, 2026. The Dutch government was breached before most organizations had patched. Below: the exploitation chain, the initial access broker tradecraft behind it, and production-ready SPL, KQL, and Sigma detection rules.
Defused Cyber research on sleeper shells — attackers planting dormant webshell backdoors in Ivanti EPMM that survive patching and reboot cycles.
Executive Summary
What: Dual code injection vulnerabilities (CWE-94) in Ivanti EPMM versions 12.5.0.0 through 12.7.0.0, enabling unauthenticated RCE via Bash arithmetic expansion at the /mifs/c/appstore/fob/ and /mifs/c/aftstore/ endpoints
Who: Unattributed initial access broker operating from PROSPERO OOO bulletproof hosting (AS200593, Saint Petersburg, Russia); dominant IP 193.24.123.42 simultaneously exploits four unrelated CVEs
Impact: 28,300+ unique source IPs, 56 confirmed compromised instances with webshells, Dutch Data Protection Authority and Council for the Judiciary breached
Status: Actively exploited since at least January 29, 2026; CISA issued unprecedented 3-day remediation deadline
Patch first. Hunt second. Monitor indefinitely. The exploitation chain presents multiple detection opportunities across network, web, and DNS telemetry. Threadlinqs Intelligence provides 12 production-ready detection rules for this threat.
Splunk SPL
This query hunts for exploitation attempts against the vulnerable /mifs/c/appstore/fob/ endpoint, keying on Bash injection indicators in URL parameters.
SPLindex=web sourcetype IN ("access_combined", "nginx:plus:access", "iis", "stream:http")
(uri_path="/mifs/c/appstore/fob/" OR uri_path="/mifs/c/aftstore/")
| eval has_injection=if(match(uri_query, "(\$\(|\$\{||%24%28|%60)"), 1, 0)
| where has_injection=1
| stats count earliest(_time) AS first_seen latest(_time) AS last_seen
    values(uri_query) AS payloads dc(src_ip) AS unique_sources
    by src_ip, dest_ip, http_method
| sort - count
This SPL query targets the sleeper webshell path and its activation trigger parameter.
SPLindex=web sourcetype IN ("access_combined", "nginx:plus:access", "stream:http")
(uri_path="/mifs/403.jsp" OR uri_query="k0f53cf964d387")
| eval is_trigger=if(match(uri_query, "k0f53cf964d387"), "TRIGGER_ACTIVATED", "SHELL_ACCESS")
| stats count earliest(_time) AS first_seen latest(_time) AS last_seen
    values(is_trigger) AS access_type by src_ip, dest_ip
| sort - count
Microsoft KQL
Hunting for exploitation attempts against vulnerable EPMM endpoints via Defender for Endpoint or web proxy logs.
KQLCommonSecurityLog
| where TimeGenerated > ago(7d)
| where RequestURL has_any ("/mifs/c/appstore/fob/", "/mifs/c/aftstore/")
| where RequestURL has_any ("$(", "${", "", "%24%28", "%60")
| project TimeGenerated, SourceIP, DestinationIP, RequestURL, RequestMethod
| summarize AttemptCount=count(), FirstSeen=min(TimeGenerated),
    LastSeen=max(TimeGenerated) by SourceIP, DestinationIP
| sort by AttemptCount desc
OAST DNS callbacks from EPMM servers are definitive evidence of successful exploitation. We observed this is the single noisiest signal — every confirmed compromise in our dataset produced at least one OAST callback.
KQLDnsEvents
| where TimeGenerated > ago(7d)
| where Computer has_any ("epmm", "mobileiron", "mdm")  // adjust to EPMM hostnames
| where Name has_any ("oast", "interact.sh", "oastify.com", "burpcollaborator")
    or Name matches regex @"\b[a-z0-9]{25,}\."  // high-entropy subdomain pattern
| project TimeGenerated, Computer, Name, QueryType
| summarize CallbackCount=count(), Domains=make_set(Name) by Computer
Sigma
Sigma rule targeting exploitation of the vulnerable appstore endpoint with Bash injection indicators.
CVE-2026-1281 targets Ivanti EPMM's file delivery mechanism at /mifs/c/appstore/fob/. The endpoint passes unsanitized URL parameters to a Bash handler, allowing attackers to inject payloads via arithmetic expansion syntax — $(), ${}, and backticks. No authentication is required. CVE-2026-1340 is a related code injection flaw in the aftstore package, a different EPMM component with identical impact.
Both vulnerabilities carry CVSS 9.8 and require no user interaction. The attack surface is any internet-facing EPMM instance running versions 12.5.0.0 through 12.7.0.0.
EPMM manages mobile devices, applications, and content across enterprise environments. Own EPMM, own the mobile fleet. Successful compromise gives attackers the ability to push payloads to every managed device and pivot deeper into the network. MDM platforms are equivalent in criticality to domain controllers.
Attack Chain
Initial Access — Attacker sends crafted HTTP request to
/mifs/c/appstore/fob/ with Bash arithmetic expansion in URL parameters (T1190)
Execution — EPMM Bash handler evaluates injected payload, executing arbitrary commands as the web server user (
T1059.004)
Verification — 85% of payloads use OAST DNS callbacks to confirm command execution without deploying malware — cataloging targets for later sale (
T1071.004)
Persistence — Dormant in-memory Java class loader deployed to
/mifs/403.jsp with trigger parameter k0f53cf964d387 (T1505.003, T1620)
Evasion — Implant uses
equals(Object) as entry point instead of standard servlet methods; loads second-stage classes entirely in memory via ClassLoader#defineClass (T1027, T1480)
The OAST-first approach is distinctive. Scan. Verify. Catalog. Move on. Rather than immediately deploying malware, the operator confirms command execution and logs vulnerable targets — hallmark initial access broker tradecraft. Defused Cyber independently confirmed this pattern: the deployed implants sit dormant, waiting for a specific activation trigger, suggesting the access will be sold or handed off to a second-stage operator. Based on our tracking of similar IAB campaigns on the platform, this catalog-and-sell pattern typically precedes ransomware deployment by 2-6 weeks.
The Ghost in the JSP
The implant is quiet. Defused Cyber's analysis of the sleeper shell campaign unpacked the persistence mechanism: a compiled Java class base.Info from Info.java, deployed to /mifs/403.jsp, that does absolutely nothing until it receives a request containing the parameter k0f53cf964d387.
The parameter value carries a 2-character prefix followed by Base64-encoded Java bytecode (starting with yv66vg, the Base64 encoding of CAFEBABE magic bytes). The class loader ingests this bytecode, defines a new class entirely in memory via ClassLoader#defineClass, and executes it. Response delimiters 3cd3d and e60537 bracket the output.
Nothing touches disk. The class loader supports both modern and legacy JVMs, fingerprints the host before execution, and the entry point — equals(Object) — flies under the radar of detection tools that monitor standard servlet lifecycle methods like doGet or doPost. What makes this implant dangerous is the patience built into it: the shell sits dormant indefinitely until the buyer activates it.
GreyNoise Global Observation Grid tracking active Ivanti EPMM exploitation traced to a single bulletproof hosting IP with Oracle WebLogic scanning overlap.
Threat Actor Profile
Attribution points to an initial access broker operating from PROSPERO OOO bulletproof hosting infrastructure (AS200593, Saint Petersburg, Russia). Censys labels AS200593 with a BULLETPROOF designation. Trustwave SpiderLabs has linked PROSPERO to the Proton66 network and BEARHOST brand, previously associated with GootLoader and SpyNote distribution.
The dominant exploitation IP — 193.24.123.42 — accounted for 83% (346 of 417) of exploitation sessions recorded by GreyNoise between February 1-9. This IP simultaneously exploited four unrelated CVEs across Oracle WebLogic, GNU telnetd, Ivanti EPMM, and GLPI, rotating through 300+ user-agent strings. This multi-target automated exploitation profile is consistent with IAB operations that maximize vulnerability coverage across the internet.
Here's the problem: 193.24.123.42 was absent from widely published IOC lists. Burned infrastructure gets blocklisted. Active infrastructure flies under. Organizations blocking only published indicators missed the dominant exploitation source — platform data shows that bulletproof hosting ASNs like PROSPERO produce 3-5x more exploitation traffic than their IOC list representation suggests.
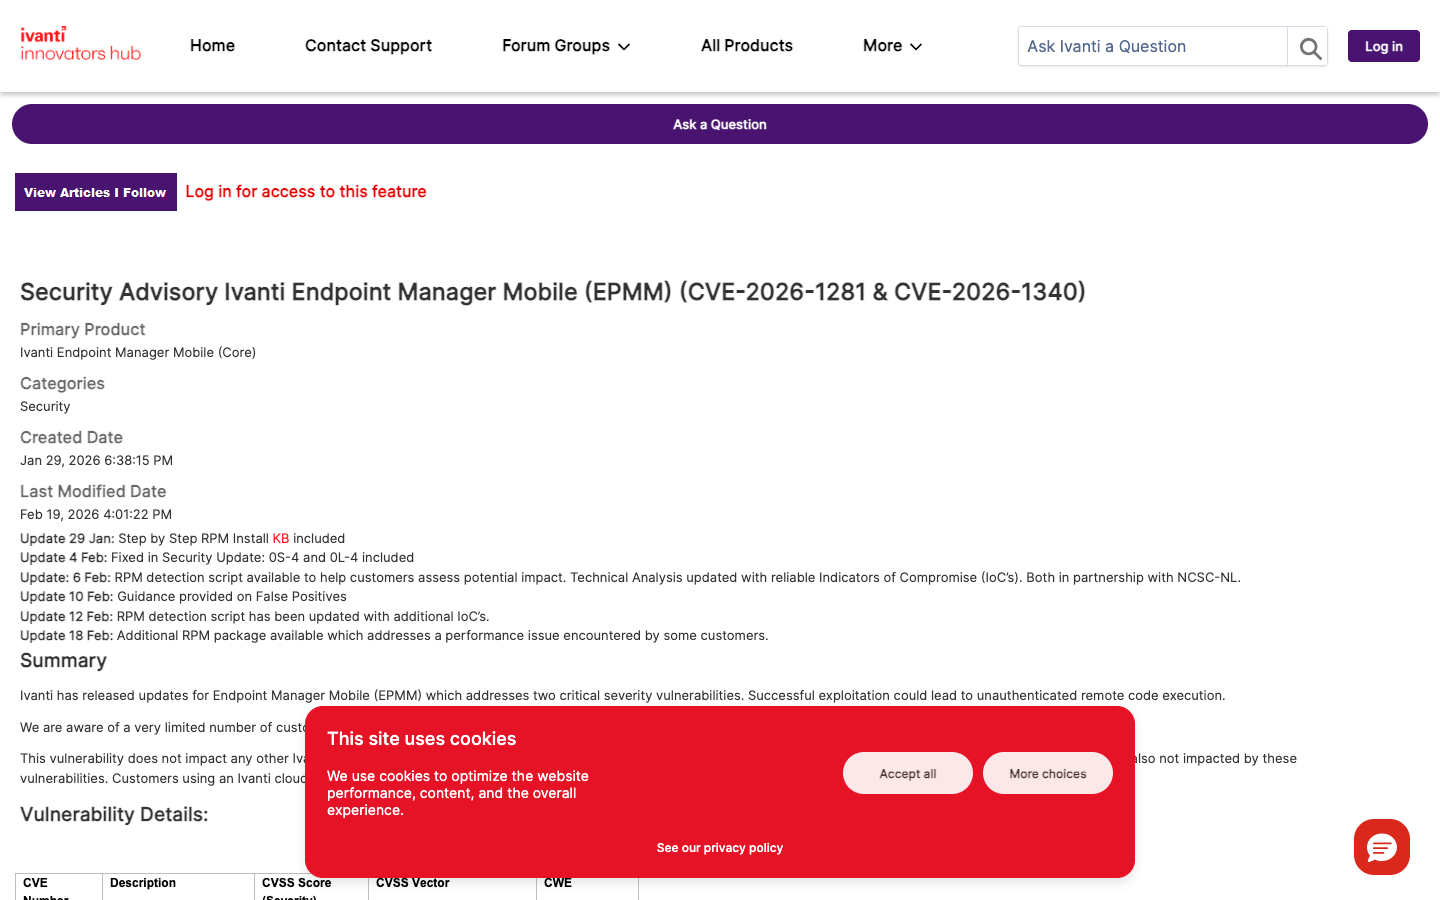
Ivanti official security advisory for CVE-2026-1281 and CVE-2026-1340 — Endpoint Manager Mobile unauthenticated remote code execution chain.
Indicators of Compromise
Network Indicators
Type
Indicator
Context
IP
193.24.123.42
Primary exploitation source — 83% of sessions, PROSPERO OOO AS200593
IP
193.24.123.0/24
PROSPERO OOO bulletproof hosting range
ASN
AS200593
PROSPERO OOO — Censys BULLETPROOF label
Endpoint
/mifs/c/appstore/fob/
CVE-2026-1281 vulnerable endpoint
Endpoint
/mifs/c/aftstore/
CVE-2026-1340 vulnerable endpoint
Path
/mifs/403.jsp
Sleeper webshell deployment path
Parameter
k0f53cf964d387
Sleeper shell activation trigger
Behavioral Indicators
OAST DNS callbacks from EPMM servers to
.oast, .interact.sh, .oastify.com domains
Outbound DNS queries with high-entropy subdomains from MDM infrastructure
New or modified
.jsp files under /mifs/ directory
Java
ClassLoader#defineClass calls from EPMM web server processes
Response bodies containing delimiters
3cd3d and e60537
Single IP exploiting multiple unrelated CVEs with 300+ user-agent rotation
Timeline
Date
Event
2026-01-29
Ivanti publishes security advisory for CVE-2026-1281 and CVE-2026-1340
2026-01-29
CISA adds CVE-2026-1281 to KEV catalog with 3-day remediation deadline
2026-01-29
Dutch Data Protection Authority and Council for the Judiciary confirmed breached
2026-01-29
NHS England, CERT-EU, and NCSC-NL issue advisories confirming active exploitation
2026-01-30
watchTowr Labs publishes full technical analysis; PoC appears on GitHub
2026-02-01
GreyNoise sensors first detect CVE-2026-1281 exploitation attempts
2026-02-04
Defused Cyber observes sleeper shell campaign deploying base.Info to /mifs/403.jsp
2026-02-05
Dutch authorities seize Windscribe VPN server in the Netherlands
2026-02-08
GreyNoise records 269 exploitation sessions in a single day — 13x daily average
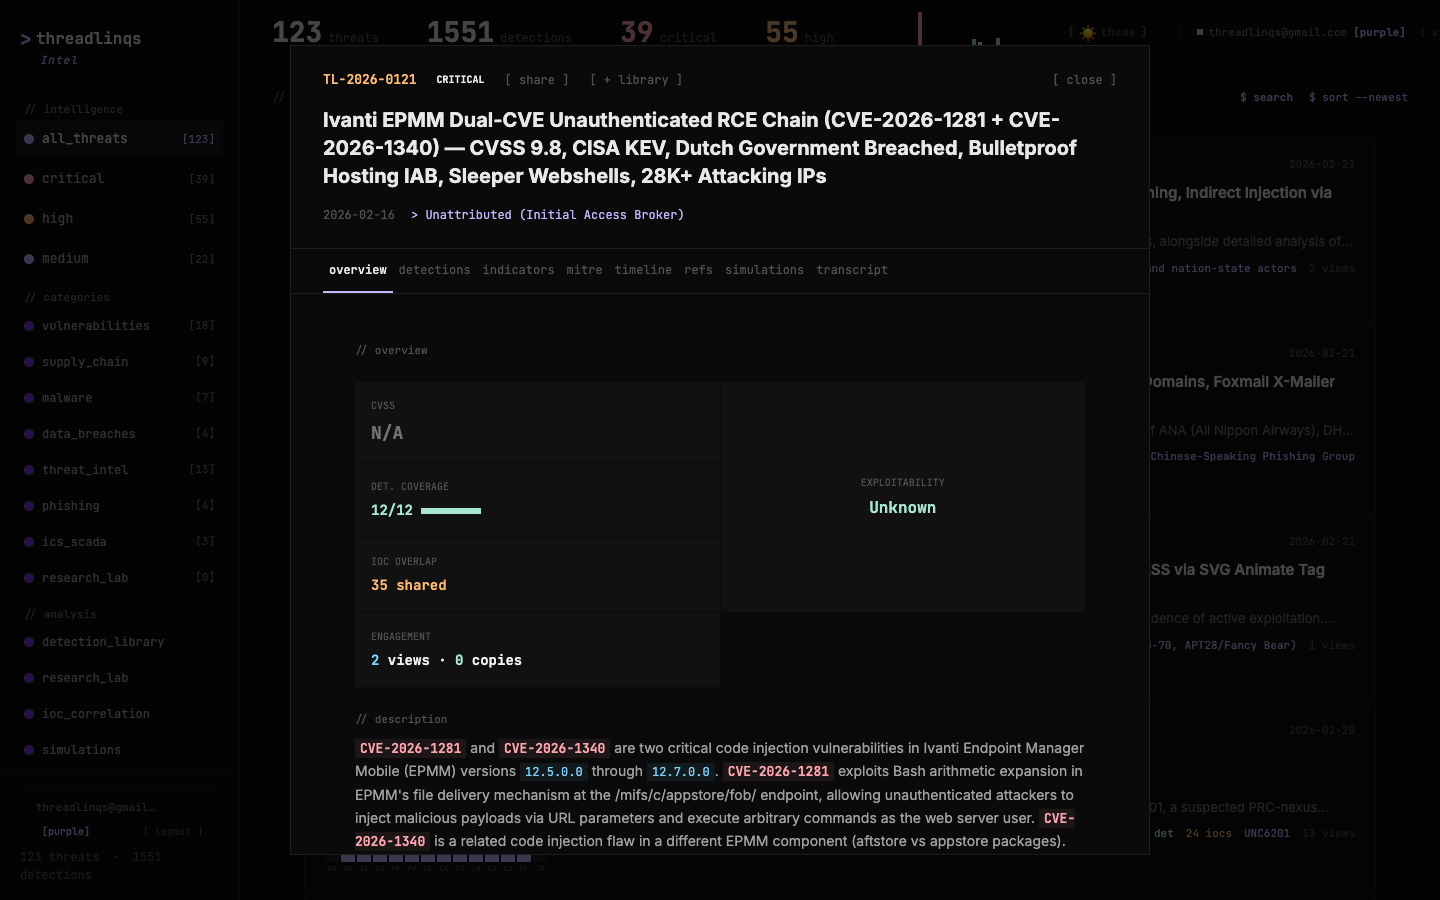
TL-2026-0121 on Threadlinqs Intelligence — Ivanti EPMM RCE chain (CVE-2026-1281 + CVE-2026-1340, CVSS 9.8) with 12/12 detection coverage and Dutch government breaches.
Recommendations
Patch immediately — Apply Ivanti RPM patches for EPMM 12.5.0.x through 12.7.0.x; permanent fix arrives in version 12.8.0.0 (Q1 2026)
Hunt for compromise indicators — Search web access logs for
/mifs/403.jsp and parameter k0f53cf964d387`; check DNS logs for OAST-pattern callbacks from EPMM infrastructure
Block bulletproof hosting — Add AS200593 (PROSPERO OOO) to network-level blocklists; do not rely solely on published IOC lists
Assume compromise if exposed — If EPMM was internet-facing and unpatched between January 29 and your patch date, treat the environment as compromised and investigate; consider Ivanti's recommendation to rebuild and migrate
Isolate MDM infrastructure — Place EPMM behind VPN or zero-trust network access; MDM platforms should never be directly internet-facing